‹ NexfolioQuality report QR-26-00039
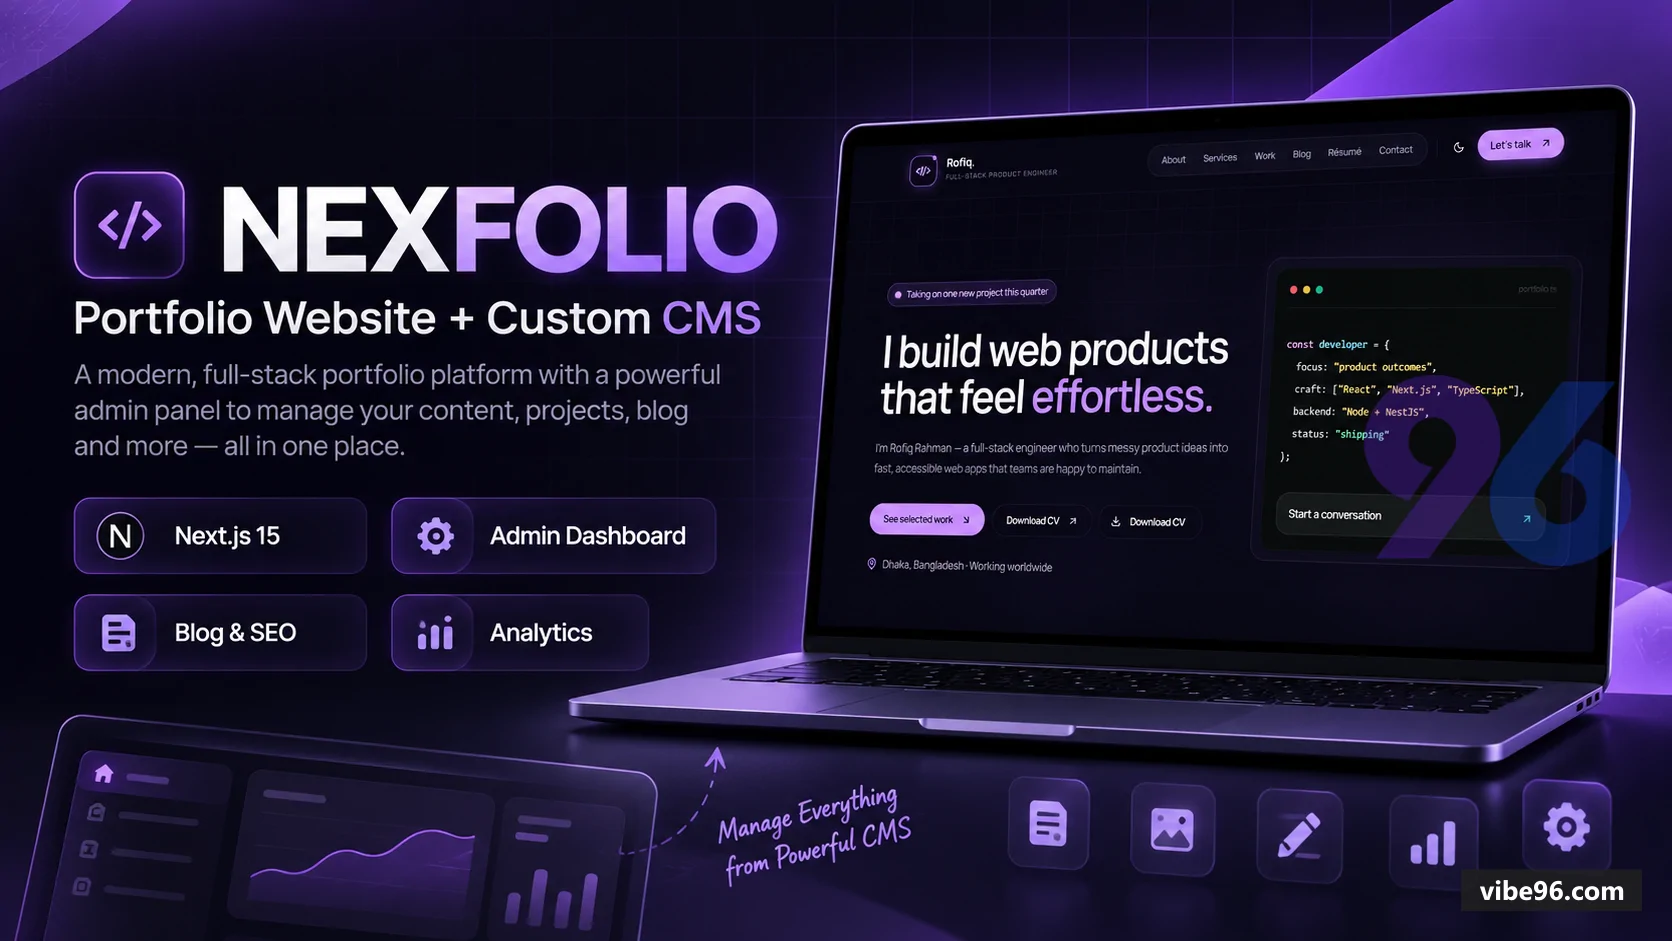
Nexfolio
Full-stack developer portfolio with admin panel, blog, resume builder, media library and visitor analytics
- Product ID
- B0063-46032
- Builder
- Shafiqul Islam Sagor
- Version reviewed
- 1.0.0 · released 18 Oct 2026
- Stack
- Next.js 15.5.7 (App Router, React 19) · TypeScript 5 · MongoDB 4.4+
- Built with
- OpenAI Codex, Claude Code, Gemini CLI
- Review period
- 18 Oct 2026 – 19 Oct 2026 · 2 rounds of changes
- ✓AI code audit6 checks · 18 Oct 2026
- ✓Installed & run19 Oct 2026
- ✓Demo vs delivered19 Oct 2026
- ✓Final sign-off19 Oct 2026
At a glance
- ✓Installed and run from the delivered code — 8 of 8 checks answered yes.
- ✓Live demo compared with the delivered code — 7 of 7 checks answered yes.
- !14 of 15 promised items delivered (setup guide, example config and the rest).
- ✓Security scored 96/100 with no failing check.
- !3 open warnings — explained in part 1.
AI code audit
The full source archive was read by our AI auditor against each check. It reads the code — it does not run it; running it is part 2.
| Check | What we found | Score | Result |
|---|---|---|---|
| Secrets & credentials | All scanned files contain only placeholder values, test fixtures, or environment variable references. The .env.example correctly shows template format without real credentials. Test files use hardcoded test passwords which is acceptable for unit tests. No API keys, database credentials, or signing secrets are committed. | 100 | Pass |
| Dependency vulnerabilities | All production dependencies are pinned in pnpm-lock.yaml with no known critical vulnerabilities. Package versions are current as of early 2025. A few packages could be updated to latest patch versions, but none pose security risks. | 95 | Pass |
| Authorisation & access control | All admin mutations are wrapped with adminAction() which enforces authentication and role checks. Passwords use scrypt hashing. The middleware blocks unauthenticated /admin access. Two minor gaps: visitor detail endpoint (app/admin/(panel)/visitors/[id]/page.tsx) and message detail (app/admin/(panel)/messages/[id]/page.tsx) lack explicit ownership checks, allowing any admin to view any visitor/message by ID manipulation. | 95 | Warning |
| Database access rules | The project uses Mongoose ODM with proper schema validation and no raw query concatenation, eliminating SQL injection risk. However, MongoDB lacks enforced foreign key constraints and several collections are missing indexes on reference fields (userId, projectId, postId), which could cause N+1 queries and slow lookups at scale. The schema is complete and can be created from empty. | 92 | Warning |
| Code structure & duplication | The codebase demonstrates good separation of concerns with clear module boundaries (auth, db, services, admin actions). However, there is notable duplication in validation schemas, some repetitive form components, and a few files approaching complexity limits. The architecture is sound but could benefit from schema consolidation and component extraction. | 78 | Warning |
| Build reproducibility | The project is fully buildable from source with clear package.json scripts and Docker support. All dependencies resolve correctly and no build artifacts are committed. Minor documentation gaps exist: README.md lacks explicit Node.js version requirement (only in package.json engines field) and the initial admin account creation step could be clearer for first-time users. | 92 | Pass |
Open warnings
Problems that did not stop the listing. They stay on the product page until a later version fixes them.
All admin mutations are wrapped with adminAction() which enforces authentication and role checks. Passwords use scrypt hashing. The middleware blocks unauthenticated /admin access. Two minor gaps: visitor detail endpoint (app/admin/(panel)/visitors/[id]/page.tsx) and message detail (app/admin/(panel)/messages/[id]/page.tsx) lack explicit ownership checks, allowing any admin to view any visitor/message by ID manipulation.
The project uses Mongoose ODM with proper schema validation and no raw query concatenation, eliminating SQL injection risk. However, MongoDB lacks enforced foreign key constraints and several collections are missing indexes on reference fields (userId, projectId, postId), which could cause N+1 queries and slow lookups at scale. The schema is complete and can be created from empty.
The codebase demonstrates good separation of concerns with clear module boundaries (auth, db, services, admin actions). However, there is notable duplication in validation schemas, some repetitive form components, and a few files approaching complexity limits. The architecture is sound but could benefit from schema consolidation and component extraction.
Requirement list
What the builder agreed to deliver before uploading — 14 of 15 met.
- Complete source for every component Met
- No real credentials in the archive Met
- Builds from a clean machine Met
- Database script or migrations Met
- Authentication and roles on every mutating endpoint Met
- Pinned dependencies without critical CVEs (nice)Partial
- Documentation set (nice)Met
- Working live demo Met
- README.md Met
- HowToSetup.md Met
- CLAUDE.md (or AGENTS.md) (nice)Met
- CHANGELOG.md (nice)Met
- .env.example Met
- a project file Met
- a project file (nice)Met
Human review
Reviewers from the Vibe96 team in Dubai worked through each question below; a final reviewer signed it off.
Stage 1 — Installed and run from the delivered code
Completed 19 Oct 2026A reviewer installed the product on a clean machine, following only the guide that ships with it.
| Question | Answer | Reviewer's note |
|---|---|---|
| Packages restored without errors | Yes | |
| Solution builds clean | Yes | |
| Database created from the shipped script or migrations | Yes | |
| First sign-in works with the documented steps | Yes | |
| Setup guide is accurate and complete | Yes | |
| Every module in the feature list opens and works | Yes | |
| No real secrets in the archive | Yes | |
| Branding and company details can be changed without code | Yes |
Stage 2 — Live demo compared with the delivered code
Completed 19 Oct 2026A second reviewer checked that what the listing and demo show is what the buyer receives.
| Question | Answer | Reviewer's note |
|---|---|---|
| Demo URL is reachable | Yes | |
| Demo credentials work | Yes | |
| Demo runs the same version as the archive | Yes | |
| All five differentiators are visible in the demo | Yes | |
| Screenshots match the demo | Yes | |
| Nothing in the demo is missing from the code | Yes | |
| Datasheet claims are accurate | Yes |
Changes asked for during review
- None — approved on the first round.
- Sign-off: approved for sale on 19 Oct 2026 with 3 warnings shown publicly.
What this report covers — and what it doesn't
- It covers version 1.0.0 exactly as the buyer downloads it: the source archive, the setup guide and the live demo on the dates above.
- It is not a penetration test, a performance or load test, or a legal review of third-party package licences.
- Scores are a point in time. Libraries age; a later version is audited again and gets its own report.
- Your setup matters. Hosting, configuration and changes made after purchase are outside this review.
- How the score is made: each AI check is scored 0–100 and weighted (security counts most). A listing needs 75 or more, no failing check, and the human review passed.
- Always try the live demo before buying, and ask the builder questions from the product page.
Vibe96 FZ-LLC, Dubai, UAE. This report describes the product at the time of review and is not a warranty.